
Firewall, endpoint and compliance work for Kenyan SACCOs, banks and businesses.
We install and support WatchGuard firewalls, set up endpoint protection, run systems audits against the Data Protection Act, and train your ICT staff to manage it all after we leave.
Who we usually work with
- SACCOs
- FOSA and BOSA systems, firewall setup, and data protection compliance audits.
- Banks and financial institutions
- AML and antifraud deployment, endpoint security, and vulnerability assessments.
- Businesses
- WatchGuard firewalls, endpoint protection, CRM work, and staff training.
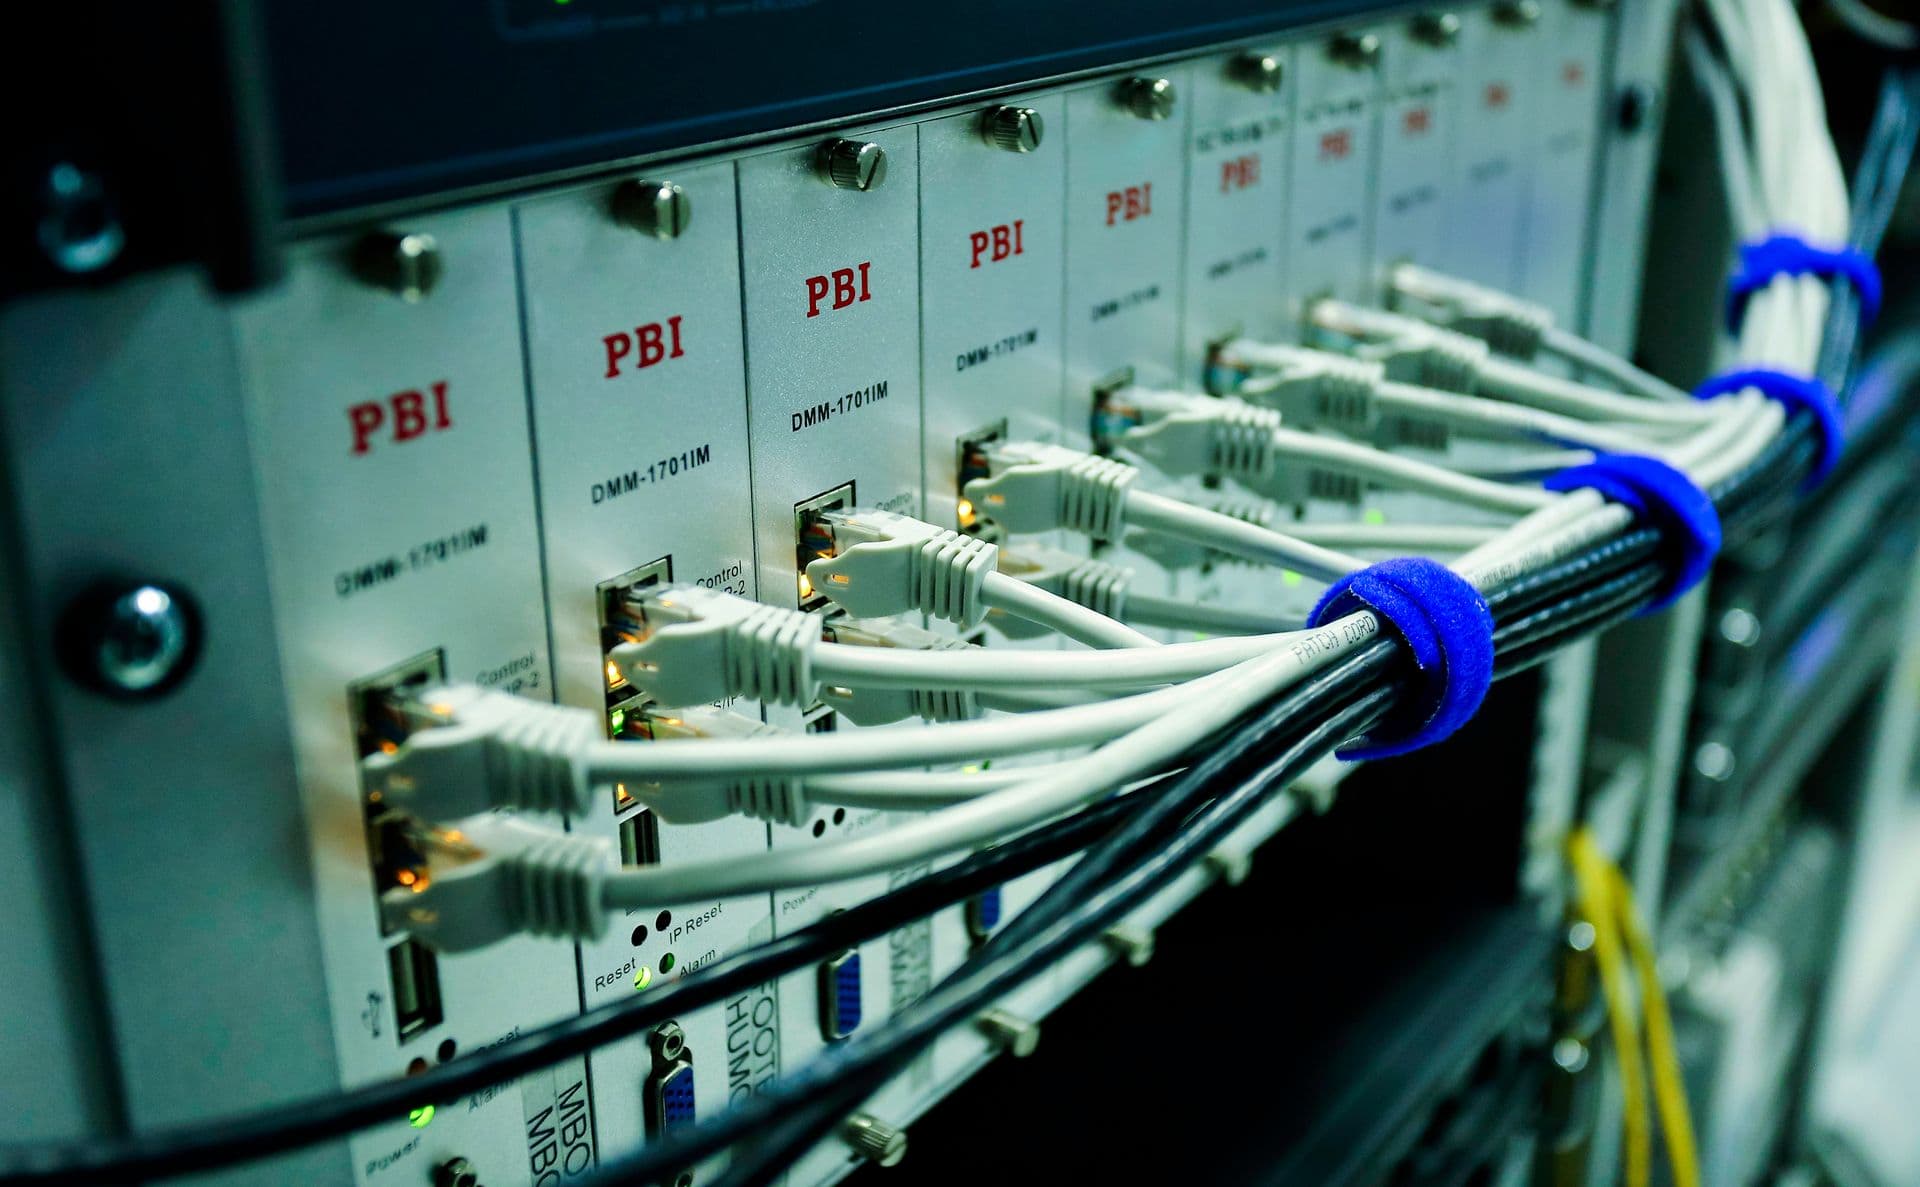
Firewall and network setup
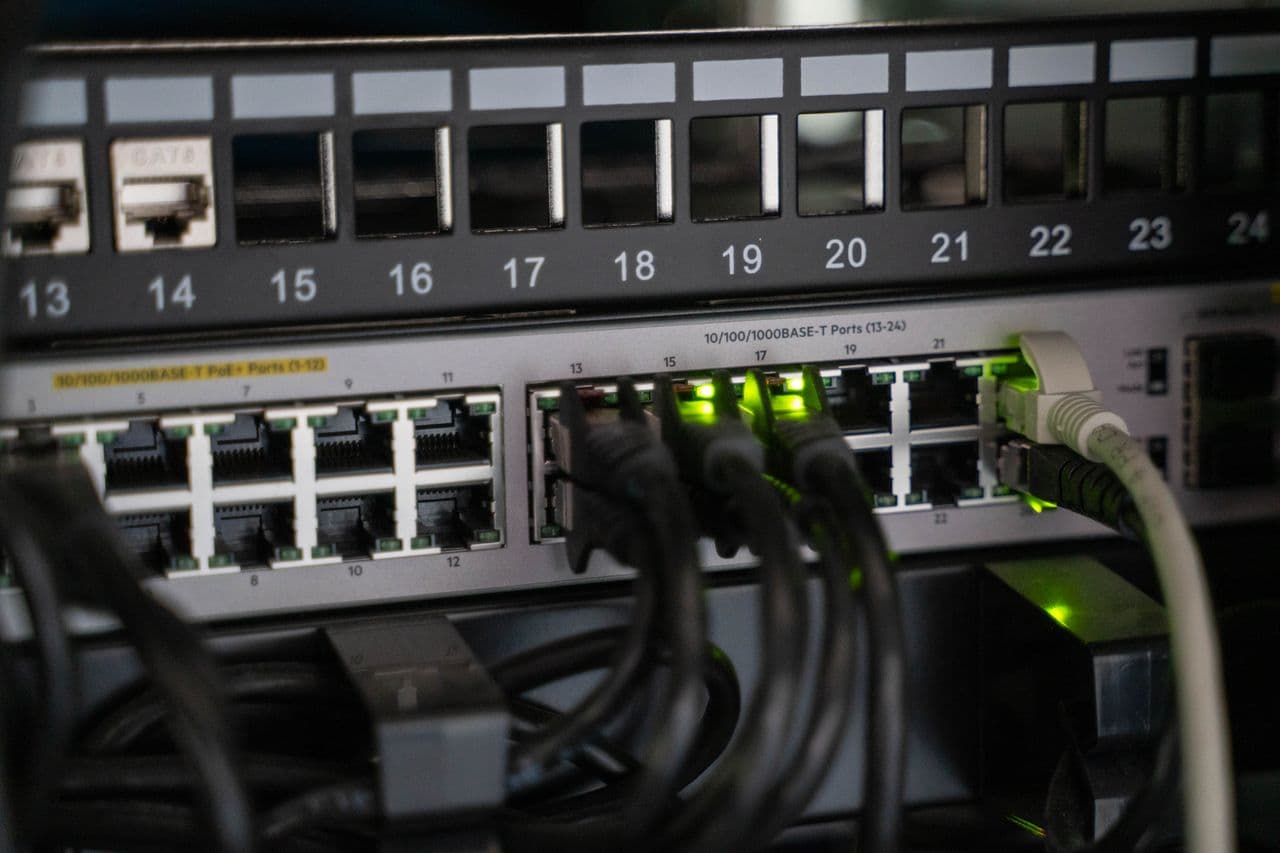
We configure WatchGuard firewalls and tidy up the network behind them.
What we do
Most of these we deliver together for the same client.
Firewall Deployment & Support
WatchGuard NGFW configuration, deployment, and ongoing support at your network edge.
Read more
Endpoint Security
Corporate endpoint protection setup and support, with post-training for your admin team.
Read more
AI-Driven Security Automation
Automated threat detection and monitoring, plus training your team to run it.
Read more
Systems Audit
Technical audits and vulnerability assessments of your network, servers and devices.
Read more
Governance, Risk & Compliance (GRC)
ICT policies, risk assessments and compliance work for regulated organisations.
Read more
Software Provision Solutions
Supply, licensing, installation and support of business and security software.
Read more
Custom Systems (FOSA & BOSA)
Systems built and customized for SACCO front and back office operations.
Read more
AML & Antifraud Solutions
Deployment support for anti-money-laundering and antifraud tooling in financial institutions.
Read more
Training & E-Campus
Technical training for staff and students in AI automation, GRC, data protection, and cybersecurity.
Read moreHow we work
Most engagements follow these four steps, from the first audit to ongoing support.
Step 01
Assess
Systems audit, vulnerability scan, and compliance check against local data protection requirements.
You get: Written audit report
Step 02
Deploy
Firewall, endpoint protection, and any custom systems (FOSA/BOSA, CRM, AML tooling) configured for your environment.
You get: Systems configured and running
Step 03
Train
We train your team on the tools and automation we set up, so you are not left to figure it out alone.
You get: ICT staff who can run it
Step 04
Monitor
Ongoing AI-driven threat detection and support as your systems and risks evolve.
You get: Ongoing support
What we see while monitoring feeds into the next assessment.
Get in touch
Tell us a bit about your network and what you need. We reply by email or phone, usually within one working day.